ILIAS 11.5 on AWS User Guide
Overview
This guide covers launching and using ILIAS 11.5 on Ubuntu 24.04 from cloudimg on Amazon EC2. It is one version of the cloudimg Hardened Moodle & E-Learning Platforms AMIs listing on AWS Marketplace; you pick it as the software version when you subscribe and launch. The other learning platforms in the listing are described on the listing's guide hub.
ILIAS is an open source learning management system developed by the ILIAS open source e-Learning society: courses and groups, a content repository, SCORM and xAPI content, tests and assessments, exercises with peer review, wikis, blogs, portfolios, learning sequences, competence management and certificates. ILIAS is licensed under the GNU General Public License version 3 (GPL-3.0).
The image ships with ILIAS already installed and its database schema in place, so you sign in and start building courses. No courses, users or content are seeded beyond the single administrator account; your platform's content is yours to create.
What is on the image:
- ILIAS 11.5, installed from the sha256-pinned upstream release (the licence is verified to be the verbatim GPL-3.0 text at build time)
- HTTPS from first boot: Apache serves the site on port 443 with a certificate created on your instance's first boot, and port 80 permanently redirects to HTTPS. ILIAS's setup is command-line only (no web installation wizard exists in ILIAS 11), and the
setupandclipaths are additionally denied over HTTP - MariaDB on localhost only (utf8mb3, as ILIAS requires); ILIAS connects over the local socket as
www-datawith socket authentication, so there is no database password anywhere on the image - PHP 8.3 (FPM) with every ILIAS-required extension, including ImageMagick built from current upstream source
ilias-firstboot.service, which runs before Apache may start and mints your instance's administrator password, URL-signing keys, installation identifiers and TLS certificateilias-set-hostname, which moves the site to your own DNS name, andilias-cron.timer, which runs ILIAS's scheduled jobs- The published default credential (
root/homer) is never live: it is replaced during the build and the per-instance administrator password is minted on your instance's first boot
Default user: ubuntu · Architecture: x86_64 · Root volume: 20 GiB gp3
Security posture
- No default login. The administrator password is generated on your instance's first boot and written to a root-only file. The ILIAS published default (
root/homer) does not verify against the shipped hash. - HTTPS from first boot with a per-instance self-signed certificate; port 80 redirects to HTTPS.
- No database password. MariaDB listens on
127.0.0.1only and authenticates ILIAS'swww-dataaccount by the local socket. - Exact ports. Only 22 (SSH), 80 (redirect) and 443 (HTTPS) listen on a public address.
- No metadata access for the application. Apache, PHP-FPM, MariaDB and the cron job are denied the instance metadata service (169.254.169.254); only the first-boot and base-URL helpers may read it, to learn the instance's address.
- Forged host names are refused so links ILIAS builds in e-mail cannot be poisoned, and client-supplied forwarding headers are stripped so audit logs and rate limits see the real client.
Prerequisites
- An AWS account subscribed to the listing.
- An EC2 key pair for SSH.
- A security group allowing inbound 22 from your management network and 443 (and 80 for the HTTPS redirect) from your users.
- A recommended instance type of
m5.largeor larger for production.
Step 1: Launch from AWS Marketplace
Subscribe to the listing, choose ILIAS 11.5 on Ubuntu 24.04 as the version, and launch with your key pair and security group. Wait for the instance status checks to pass, then give first boot a minute to mint your credentials.
Step 2: Launch from the AWS CLI
aws ec2 run-instances \
  --image-id <ami-id> \
  --instance-type m5.large \
  --key-name <your-key> \
  --security-group-ids <your-sg> \
  --block-device-mappings 'DeviceName=/dev/sda1,Ebs={VolumeSize=20,VolumeType=gp3}' \
  --metadata-options 'HttpTokens=required' \
  --tag-specifications 'ResourceType=instance,Tags=[{Key=Name,Value=ilias}]'
Step 3: Connect over SSH
ssh -i <key.pem> ubuntu@<public-dns>
The login user is ubuntu.
Step 4: Retrieve your credentials
First boot writes your instance's credentials to a root-only file:
sudo cat /root/ilias-credentials.txt
It looks like this (your values differ):
ilias.admin.user=root
ilias.admin.pass=<generated-per-instance>
ilias.client.id=ilias
The administrator username is root (ILIAS's own administrator login name, not the Linux root user). First boot takes the site address from /etc/cloudimg/ilias-hostname if that file exists, otherwise from IMDSv2: the instance's public DNS name, else its public IPv4 address, else its private IPv4 address. If you keep credentials centrally, copy them into AWS Secrets Manager.
Step 5: Verify the services
systemctl is-active apache2 php8.3-fpm mariadb
ls /var/lib/cloudimg/ilias-firstboot.done
All three services print active, and the first-boot marker exists (first boot runs once; after a reboot its unit shows as skipped, which is expected). Only 22, 80 and 443 listen on a public address; MariaDB is on 127.0.0.1:3306:
sudo ss -Hltn | awk '{print $4}' | sort -u
The HTTPS front end on the configured name answers, and port 80 redirects to HTTPS:
SITE=$(cat /var/lib/cloudimg/ilias-address)
curl -sk -o /dev/null -w "%{http_code}\n" --resolve "${SITE}:443:127.0.0.1" "https://${SITE}/login.php?client_id=ilias&cmd=force_login"
curl -s -o /dev/null -w "%{http_code} %{redirect_url}\n" --resolve "${SITE}:80:127.0.0.1" "http://${SITE}/"
MariaDB holds no password. Every account uses socket authentication or is locked, and ILIAS's own connections arrive over the socket as www-data:
sudo mariadb -e "SELECT User, Host, plugin FROM mysql.global_priv;"
sudo -u www-data mariadb -u www-data -N -e "SELECT CURRENT_USER();" ilias
The application cannot reach the instance metadata service. This runs the same request from inside php8.3-fpm.service and from your shell; the first prints 000 (blocked), the second 200:
CG=$(systemctl show -p ControlGroup --value php8.3-fpm.service)
sudo bash -c "echo \$\$ > /sys/fs/cgroup${CG}/cgroup.procs; exec curl -s -m 5 -o /dev/null -w '%{http_code}\n' -X PUT -H 'X-aws-ec2-metadata-token-ttl-seconds: 60' http://169.254.169.254/latest/api/token"
curl -s -m 5 -o /dev/null -w '%{http_code}\n' -X PUT -H 'X-aws-ec2-metadata-token-ttl-seconds: 60' http://169.254.169.254/latest/api/token
Step 6: Sign in
- Open the site address (the public DNS name or IP from Step 4) in a browser. Plain
http://redirects to HTTPS. - The certificate is self-signed and unique to your instance, so the browser warns the first time. Accept it, or install a trusted certificate (Step 8).
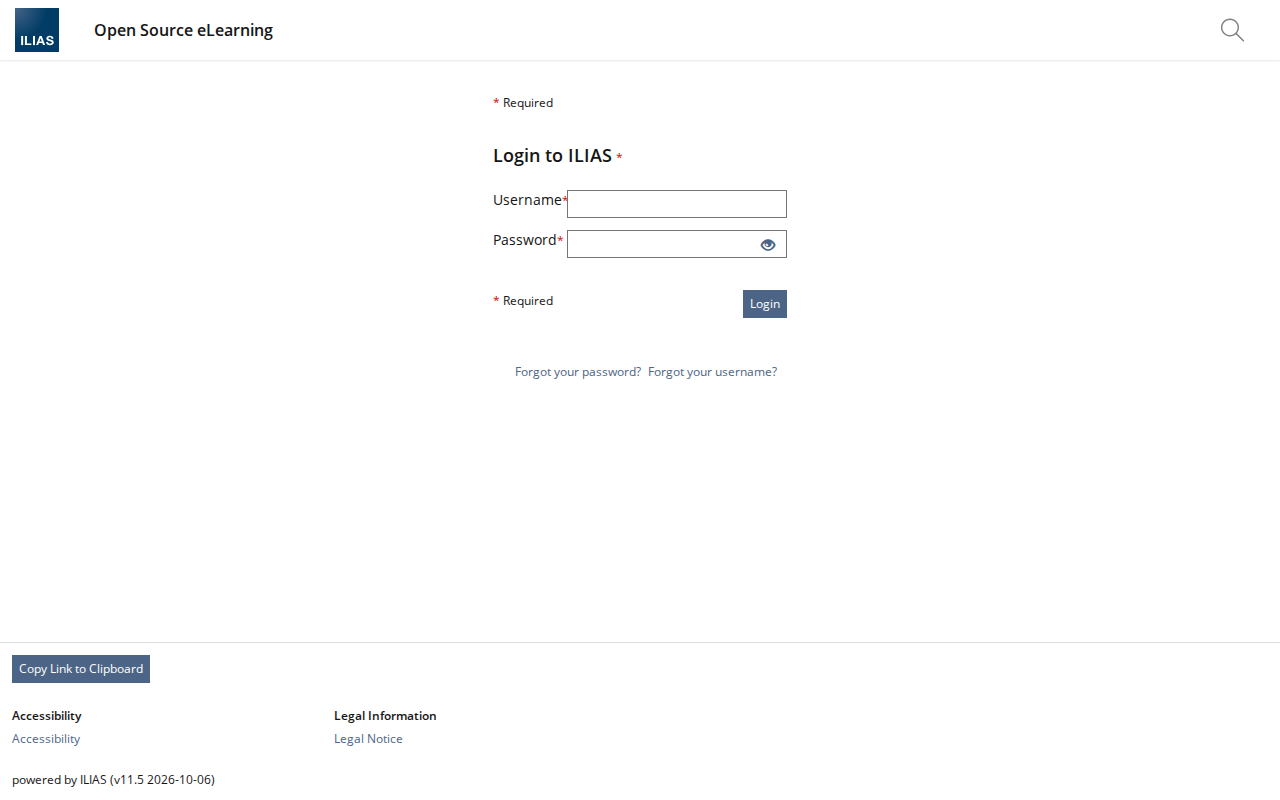
- The ILIAS sign-in form opens. Enter root as the username and the
ilias.admin.passvalue, then choose Login.
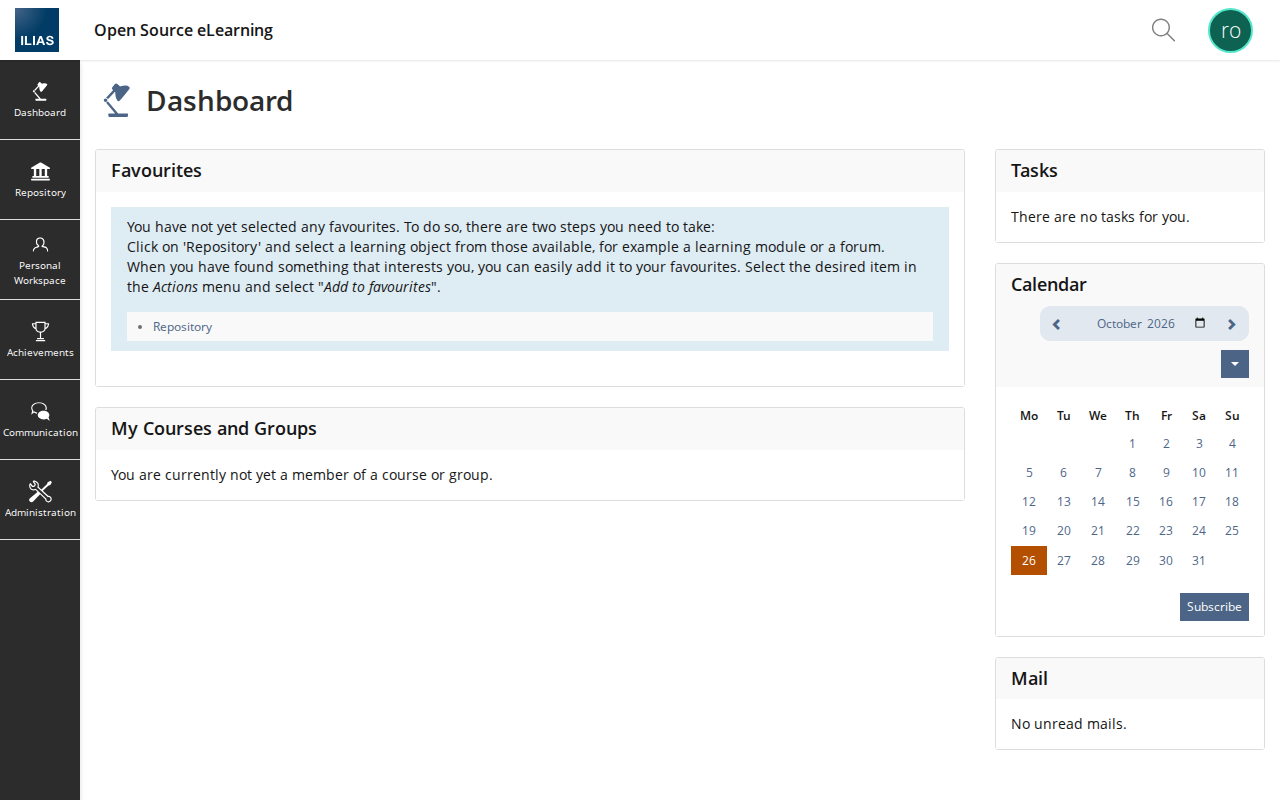
You land on the ILIAS dashboard. The main menu opens Repository, Dashboard, Achievements, Communication and the administration tools.
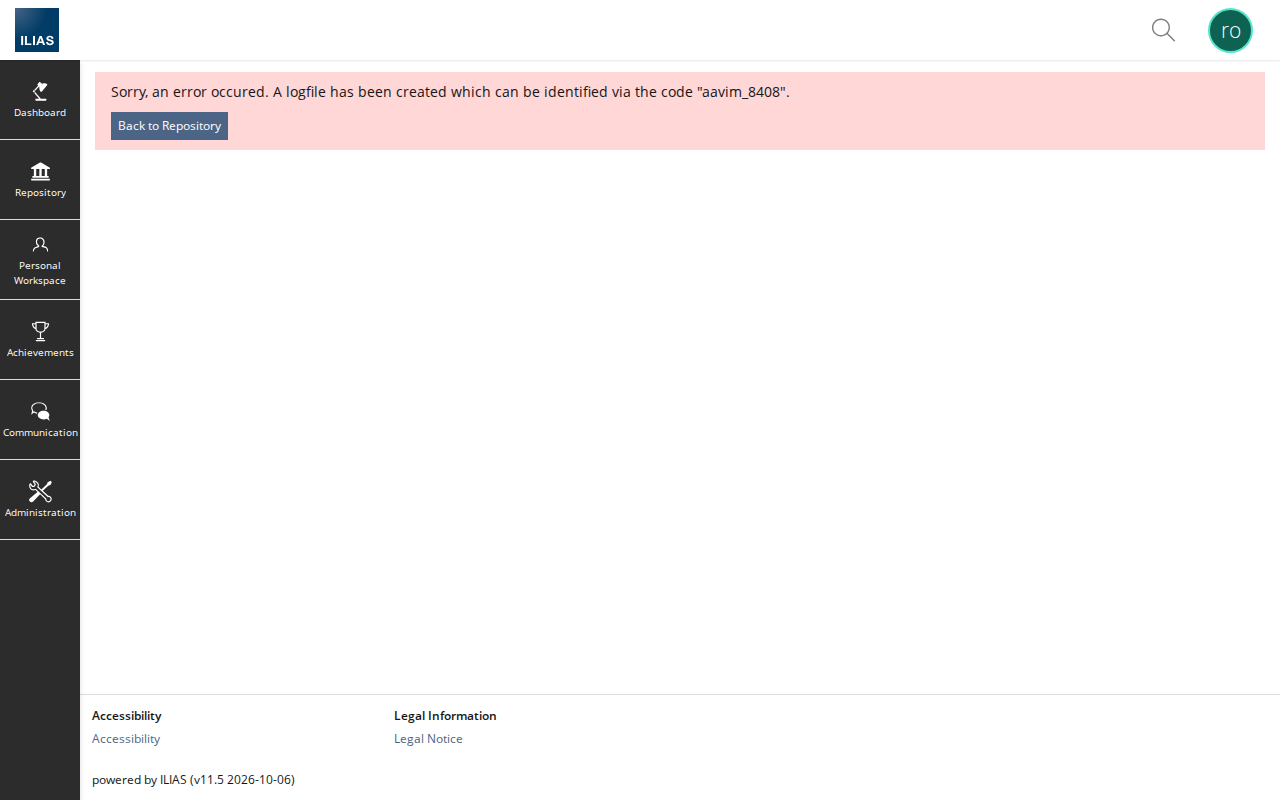
ILIAS answers only on its configured name, the instance's own IP addresses and localhost; a request naming any other host is refused.
Step 7: Use your own hostname
ILIAS builds the links in notification e-mail from its base URL, which this image sets from configuration. To serve the platform on your own DNS name, point a DNS record (for example in Amazon Route 53) at the instance's public IP (an Elastic IP keeps it stable), then run on the instance:
sudo ilias-set-hostname learn.example.org
The helper writes the name to /etc/cloudimg/ilias-hostname, issues a new self-signed certificate for it, rewrites Apache's server name and ILIAS's allowed-hosts list and base URL, and reloads Apache. An instance without an Elastic IP gets a new public DNS name when it is stopped and started; run the helper with the new name so links and the certificate follow it. Run it with --auto to return to the EC2 public DNS name.
Step 8: Install a trusted certificate
The site certificate is /etc/ssl/ilias/ilias.crt and its key /etc/ssl/ilias/ilias.key (mode 600, root). To use Let's Encrypt, first set your DNS name (Step 7), open port 80 to the internet, then:
sudo apt-get install -y certbot
sudo certbot certonly --standalone -d learn.example.org \
  --pre-hook "systemctl stop apache2" --post-hook "systemctl start apache2" \
  --deploy-hook "install -m 644 \$RENEWED_LINEAGE/fullchain.pem /etc/ssl/ilias/ilias.crt && install -m 600 \$RENEWED_LINEAGE/privkey.pem /etc/ssl/ilias/ilias.key"
certbot keeps the hooks for every renewal. Running ilias-set-hostname again replaces the certificate with a self-signed one, so run sudo certbot renew --force-renewal afterwards.
Step 9: Create your first course
- Open the main menu and choose Repository — the top of the ILIAS content tree. Use the Add New Item control to add a Course, then set its title, availability and enrolment.
- Inside the course, add content objects: files, web links, wikis, exercises, tests, learning sequences and SCORM/xAPI learning modules.
- Create user accounts under Administration → Users, or import them from a file. Self-registration is disabled by default; enable it under Administration → User Services if you want public sign-up.
- Set your administrator's e-mail address and configure outgoing mail under Administration before you rely on notifications or password resets.
Step 10: Server components
| Component | Version | Notes |
|---|---|---|
| ILIAS | 11.5 | github.com/ILIAS-eLearning/ILIAS, GPL-3.0; /var/www/ilias |
| PHP | 8.3 (FPM) | Ubuntu 24.04 packages (>= 8.3.6-0ubuntu0.24.04.13) |
| Apache | 2.4 | TLS front end on 80/443, PHP over FPM |
| MariaDB | 10.11 | localhost only; utf8mb3; socket authentication, no password |
The image updates the PHP libraries ILIAS vendors to the releases that fix their published advisories (league/commonmark 2.10.4, Symfony 6.4.48), and a build-time dependency audit fails closed on any remaining reachable advisory.
sudo mariadb ilias -N -e "SELECT value FROM settings WHERE module='common' AND keyword='ilias_version';"
php -v | head -n 1
mariadb --version
Step 11: Filesystem layout
| Path | Purpose |
|---|---|
/var/www/ilias |
ILIAS application (code; public/ is the web docroot) |
/var/www/ilias/public/data/ilias/client.ini.php |
Client configuration (mode 640; the DB password is empty — socket auth) |
/var/www/files |
ILIAS data directory (uploaded content and files) |
/var/www/logs |
ILIAS application logs |
/var/lib/mysql |
MariaDB database |
/etc/ssl/ilias/ |
Site certificate and key |
/root/ilias-credentials.txt |
Your credentials (mode 600, root) |
/var/lib/cloudimg/ilias-firstboot.done |
First-boot marker; Apache and PHP-FPM start only when it exists |
ls -ld /var/www/ilias /var/www/files /var/www/logs; df -h /
Step 12: Managing the services
systemctl status apache2 php8.3-fpm mariadb --no-pager -n 0
Restart PHP-FPM with sudo systemctl restart php8.3-fpm and reload Apache with sudo systemctl reload apache2. Logs are in /var/log/apache2/ilias-*.log and /var/www/logs/; the Amazon CloudWatch agent can ship them to CloudWatch Logs. ILIAS's scheduled jobs run from ilias-cron.timer every five minutes; run them by hand with:
sudo -u www-data php /var/www/ilias/cli/cron.php run-jobs root ilias
Step 13: Backups
Dump the database as root over the socket (no password), and keep the data directory with it:
sudo mariadb-dump --single-transaction --routines --triggers ilias > ~/ilias-$(date +%Y%m%d).sql
sudo tar -czf ~/ilias-files-$(date +%Y%m%d).tar.gz -C /var/www files
Copy both to an Amazon S3 bucket or another durable destination. An EBS snapshot of the root volume is a simple whole-platform backup:
aws ec2 create-snapshot --volume-id <root-volume-id> --description "ilias $(date +%F)"
Step 14: Troubleshooting
The browser cannot connect, or the connection is dropped. Browse to the configured name (shown as the site address); other host names are refused by design. Check that ports 80 and 443 are open in the security group.
Apache or PHP-FPM is not running after launch. Both start only after first boot completes:
ls -la /var/lib/cloudimg/ilias-firstboot.done
sudo journalctl -u ilias-firstboot --no-pager | tail -n 20
If the marker is missing, first boot did not finish. Fix the cause, then run it again:
sudo systemctl restart ilias-firstboot
sudo systemctl start php8.3-fpm apache2
Confirm the administrator login works. The published default root/homer must be rejected and your per-instance password accepted; the stored hash never verifies homer:
sudo mariadb ilias -N -e "SELECT passwd FROM usr_data WHERE login='root';" | php -r '$h=trim(fgets(STDIN)); echo password_verify("homer",$h)?"homer STILL VALID\n":"homer rejected (good)\n";'
Step 15: Security recommendations
- Keep port 22 limited to your management network.
- Change the administrator password from the ILIAS user settings if you share it, and give instructors their own accounts rather than the administrator login.
- Keep MariaDB on socket authentication. If a reporting tool must connect over the network, create a separate read-only account with its own password, bind it to the tool's address, and keep port 3306 closed in the security group.
- Apply Ubuntu security updates regularly (
sudo apt-get update && sudo apt-get upgrade); unattended security upgrades are enabled.
Step 16: Support and licensing
ILIAS is licensed under the GNU General Public License version 3 (GPL-3.0); its source is at github.com/ILIAS-eLearning/ILIAS. You are responsible for the data protection of the learner records you enter. ILIAS is a trademark of the ILIAS open source e-Learning society; cloudimg is not affiliated with or endorsed by the society.
cloudimg provides 24/7 technical support by email and live chat: support@cloudimg.co.uk. Every product in this listing is on the Hardened Moodle & E-Learning Platforms AMIs guide hub.