Base
Hardened build
minimal ports, security patches applied at build time

openSUSE Leap 16.0 with the GNOME desktop, reached over RDP: no default password, remote desktop switched off until you turn it on, and a per VM RDP credential generated at first boot.
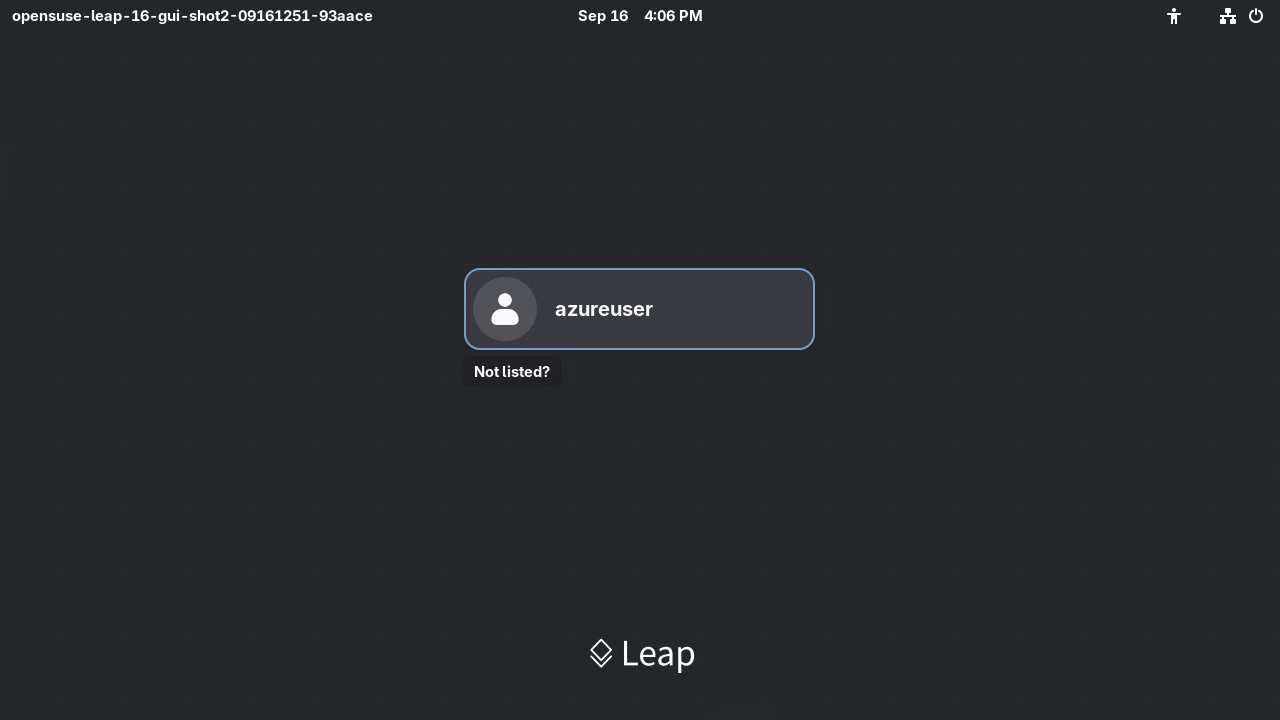
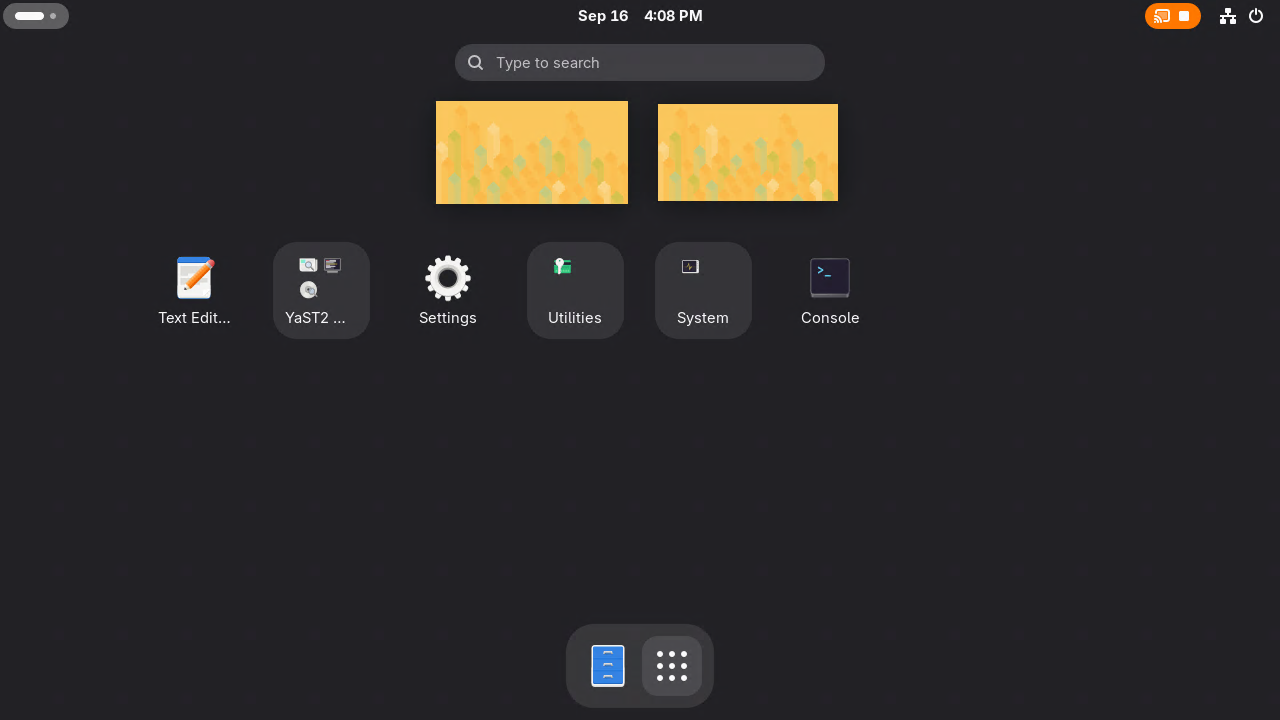
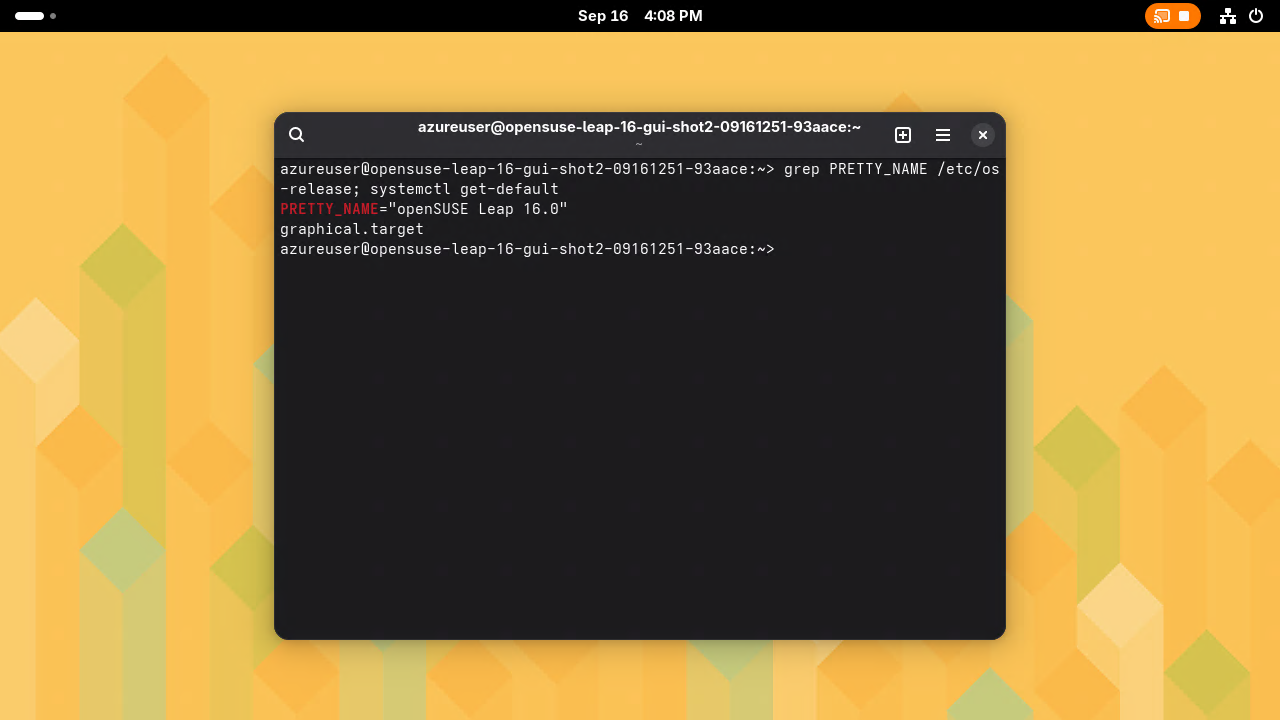
openSUSE Leap 16.0 with GNOME Desktop is openSUSE Leap 16.0, the openSUSE Project's community distribution that shares its core code base with SUSE Linux Enterprise 16, with the distribution's own desktop added: the GNOME Desktop Environment (Wayland) pattern from openSUSE's repo-oss repository. It is free to use, patch and redistribute, with no subscription and no licence key. GNOME Remote Desktop is set up for remote login, so you connect with any RDP client, the GNOME login screen appears, and you sign in to a full GNOME 48 desktop session running on the virtual machine, with Files, Console, Text Editor, System Monitor and Settings ready to use.
Remote access is first party: the RDP server is GNOME Remote Desktop, built and signed by SUSE in repo-oss, so nothing outside the distribution is added to reach the desktop. The desktop is installed from the pattern without its optional extras, so it stays lean, and anything else you need installs with zypper. The session is Wayland, with Xwayland for X applications, on a Btrfs root with SELinux enforcing.
It suits cloud workstations for openSUSE and SUSE Linux Enterprise development, graphical administration and data tools that should run close to your cloud resources, training labs that need a desktop rather than a shell, and a secure jump desktop reached only through an SSH tunnel.
cloudimg builds the desktop so that a new machine exposes nothing but SSH. Remote desktop ships switched off, no account has a password, and the RDP server cannot be enabled until you have set your own. At first boot each machine generates its own RDP credential and its own TLS certificate, readable by root only and kept out of the system journal, so nothing is shared between machines or baked into the image. The unconfigured Entra ID sign in daemon the update stream pulls in is left out, because it fails on every boot and would share a machine secret between clones. A single helper command shows the remote desktop state, turns it on and off, and prints this machine's credential. SELinux stays enforcing, SSH stays key only even after you set a desktop password, every available patch is applied at build time, and a daily zypper patch timer keeps applying security and kernel patches without ever rebooting on its own, all backed by 24/7 support.
Real screenshots taken while testing this image against its deployment guide.

Migrate from CentOS 8 EOL to Alma Linux 8 in under 60 seconds with zero licensing fees. 1:1 RHEL 8 compatible, AWS-optim...
Windows Server 2022 preconfigured with AWS tooling and 24/7 expert support behind it.
Windows Server 2025 Datacenter preconfigured for AWS, with hotpatching to trim maintenance windows.
Oracle Linux 10.0, a RHEL 10 compatible enterprise distribution, tuned for AWS and ready to run.
Available versions: Oracle Linux 8.0, 8.1, 8.2, 8.3, 8.4, 8.5, 8.6, 8.7, 8.8, 8.9, and 8.10. Each version is available a...
Available versions: Oracle Linux 8.0, 8.1, 8.2, 8.3, 8.4, 8.5, 8.6, 8.7, 8.8, 8.9, and 8.10. Each version is available a...