Base
Hardened build
minimal ports, security patches applied at build time
CAS, SAML 2.0 and OpenID Connect from one WebSSO server, with every signing key minted on your own machine
LemonLDAP::NG is a WebSSO portal and access manager. It authenticates people once and then acts as an identity provider for the applications they go on to use, and it is unusual in speaking CAS, SAML 2.0 and OpenID Connect at the same time, from the same server. That combination is what makes it the practical migration route for an organisation moving off a legacy CAS deployment: you can keep answering CAS for the applications that still need it while issuing OpenID Connect tokens and SAML assertions to everything new, without running three products. It is widely deployed across European public sector and higher education, and is free software under the GNU General Public License, version 2 or later.
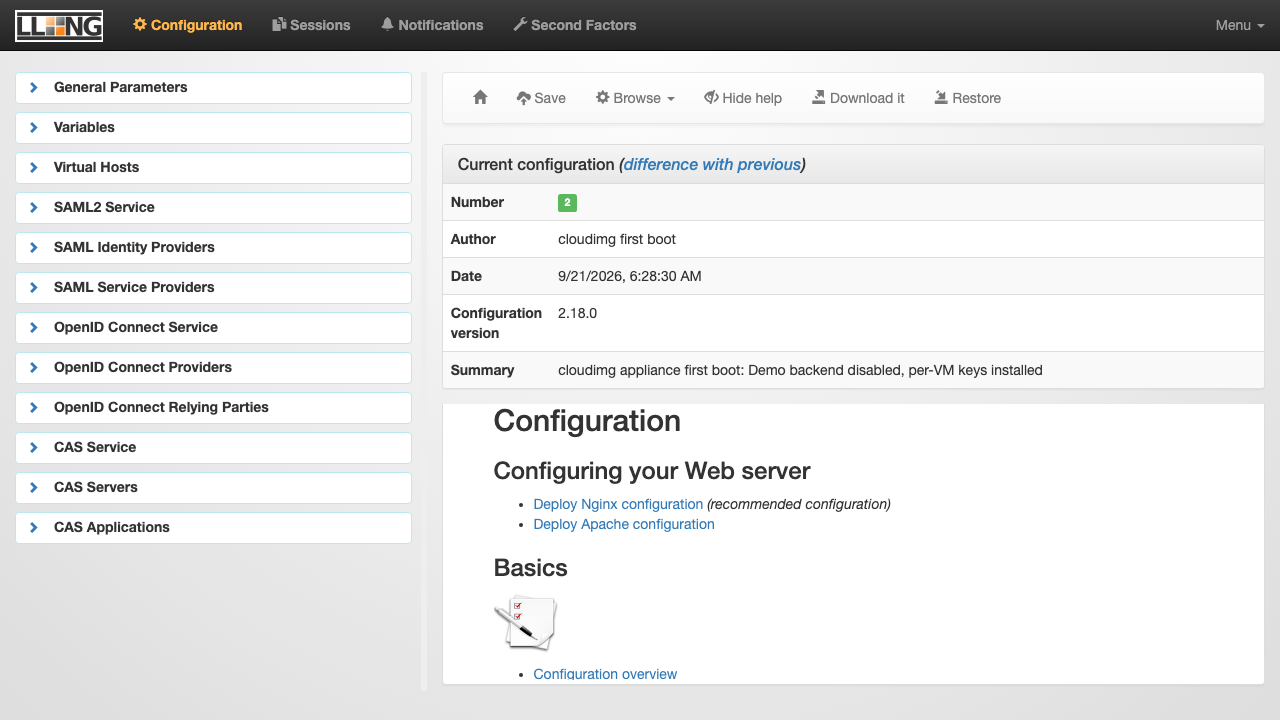
A default LemonLDAP::NG installation selects its demo authentication backend, and that backend is not a placeholder with a weak password: it accepts any user whose password matches their username, and one of the accounts it resolves is granted the Manager, the full administration console. A stock install therefore ships a working administrator. This image does not. First boot moves authentication onto a directory created on your own machine, mints a per machine administrator password, and generates the SAML signing certificate, the OpenID Connect signing key, the session cipher key and the TLS certificate there too, so no customer shares a signing key with any other. Before release the demo accounts were confirmed refused while the per machine credential signed in and reached the Manager, and two machines from the image were compared label by label with all fifteen per machine secrets differing. Off box ports are 22 and 443 only, the directory is bound to loopback, and it is paired with a deployment guide and cloudimg support. SAML is shipped with published metadata carrying this machine's own signing certificate; a full browser SAML round trip needs an external service provider and was not performed, while OpenID Connect and CAS were each proven end to end.
Real screenshots taken while testing this image against its deployment guide.

1Panel is an open source, web based control panel for managing a Linux server from the browser.

Alibaba Sentinel is a flow control, circuit breaking and real-time monitoring platform for microservices and distributed...

Apache Directory Server (ApacheDS) is an extensible, embeddable LDAP v3 and Kerberos directory server written in Java by...
Apache Dubbo is an RPC and microservice framework; this image ships the Dubbo Admin console with a ZooKeeper registry, h...

Apache Guacamole is a clientless remote desktop gateway: it delivers RDP, VNC and SSH sessions to a plain web browser, w...

Apache Seata is an open source distributed transaction solution for microservices.