Base
Hardened build
minimal ports, security patches applied at build time
SAML 2.0 single sign on for federations, with signing keys minted on your own machine
Shibboleth Identity Provider is the SAML 2.0 identity provider used across research and education federations and in the public sector. It authenticates people against your own directory and issues signed SAML assertions to the services they sign in to, so one sign in works everywhere you federate. It is open source under the Apache License 2.0.
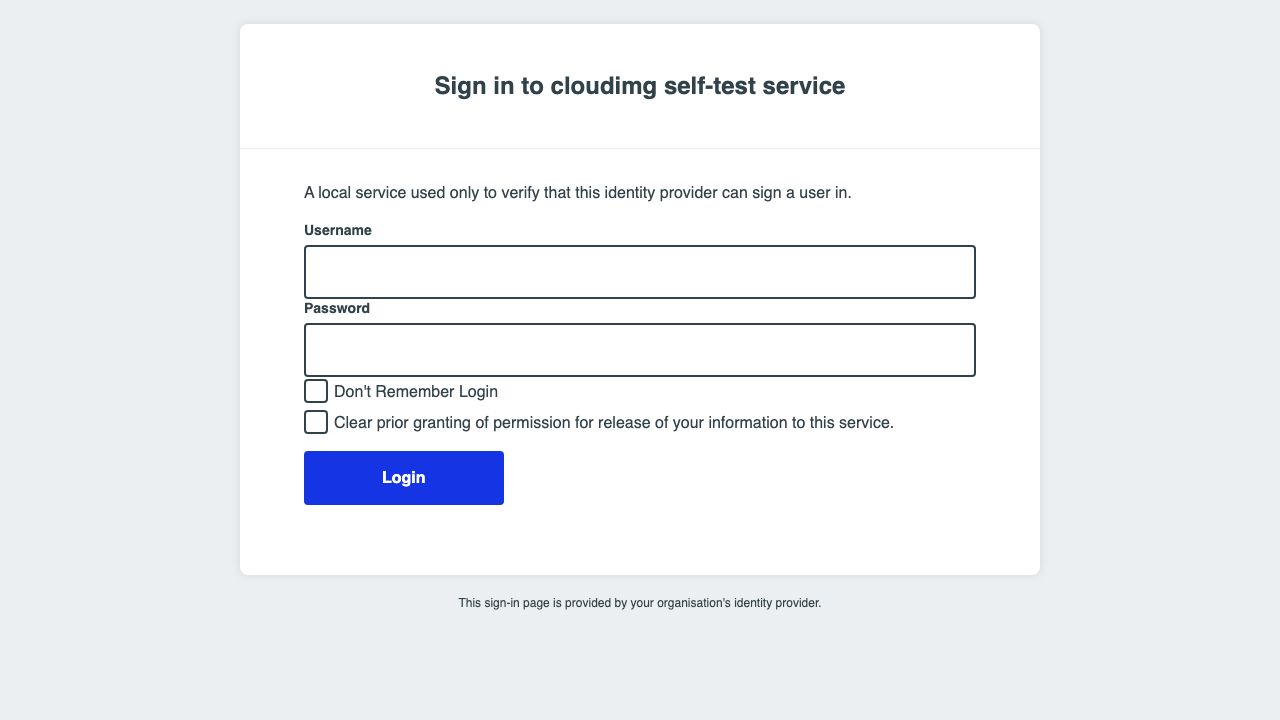
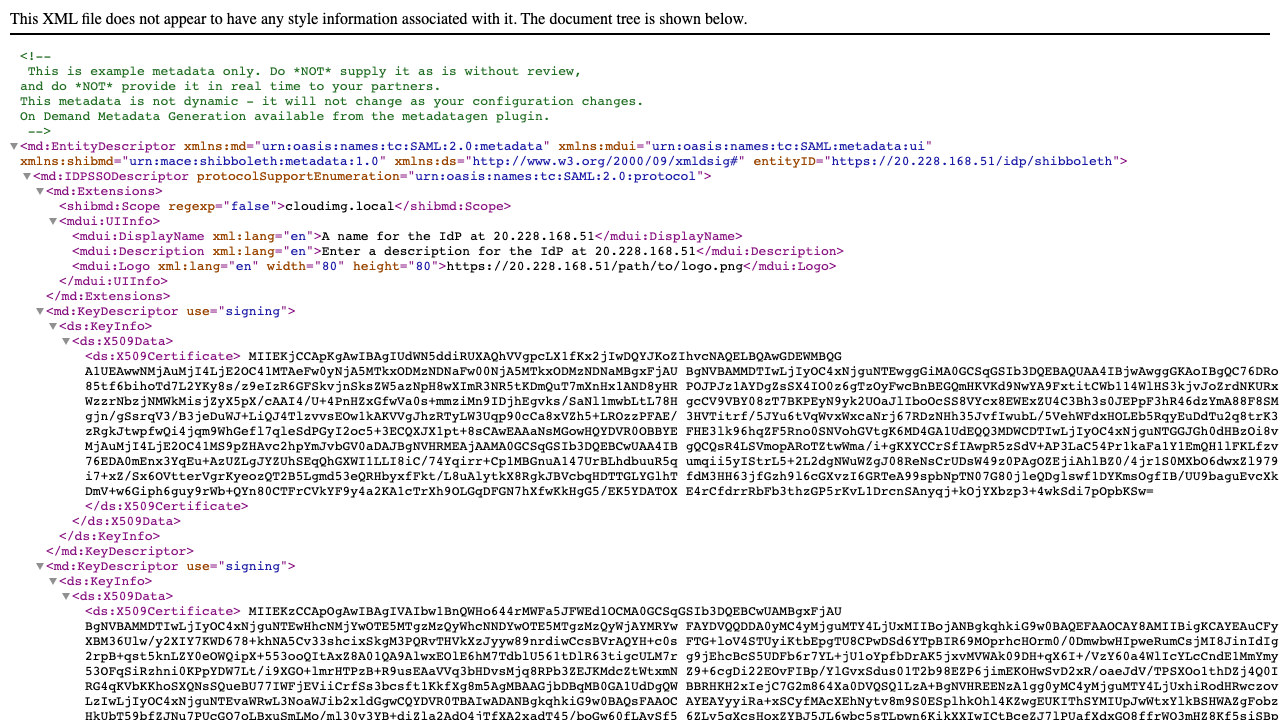
An identity provider signs assertions with a private key, and every service that trusts it trusts that key, so a key shared across an image would let any buyer impersonate any other. This image ships no installed identity provider at all: first boot runs the software's own installer and mints this machine's signing key, encryption key, sealer and published metadata. Two machines from the image were compared before release and all nineteen per machine secrets differed. A co-located directory and a self test service provider let you prove a sign in in the first minute, a per machine TLS certificate is generated at first boot, and it is paired with a deployment guide and 24/7 support.
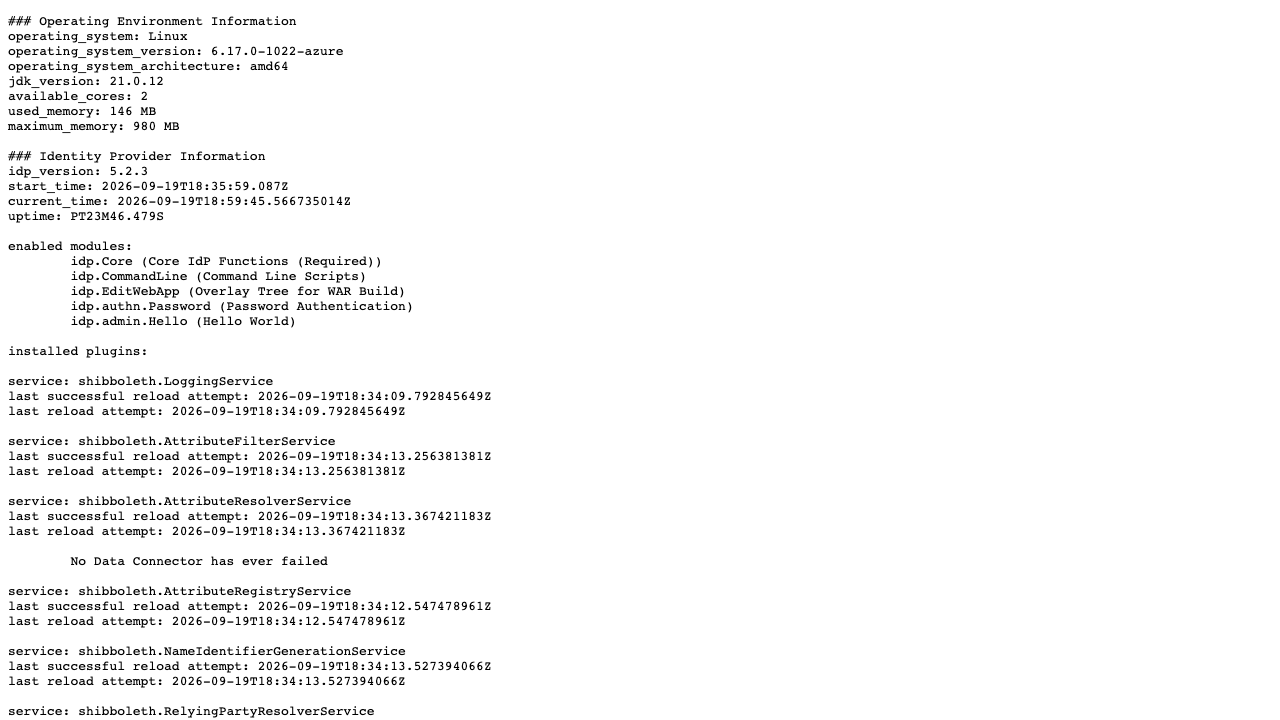
Real screenshots taken while testing this image against its deployment guide.

1Panel is an open source, web based control panel for managing a Linux server from the browser.

Alibaba Sentinel is a flow control, circuit breaking and real-time monitoring platform for microservices and distributed...

Apache Directory Server (ApacheDS) is an extensible, embeddable LDAP v3 and Kerberos directory server written in Java by...
Apache Dubbo is an RPC and microservice framework; this image ships the Dubbo Admin console with a ZooKeeper registry, h...

Apache Guacamole is a clientless remote desktop gateway: it delivers RDP, VNC and SSH sessions to a plain web browser, w...

Apache Seata is an open source distributed transaction solution for microservices.